|
A-Tec Computer Home - Repair - Malware Removal - Windows 11 - Contact - About Me - My Location - Computer Tips |
||
|
|
||
|
Scams Are Everywhere Below are two examples of warnings that are designed to scare you enough to call the phone number. Don't do this. You can also fall victim to creative email scams. More about this below. Fake warning:
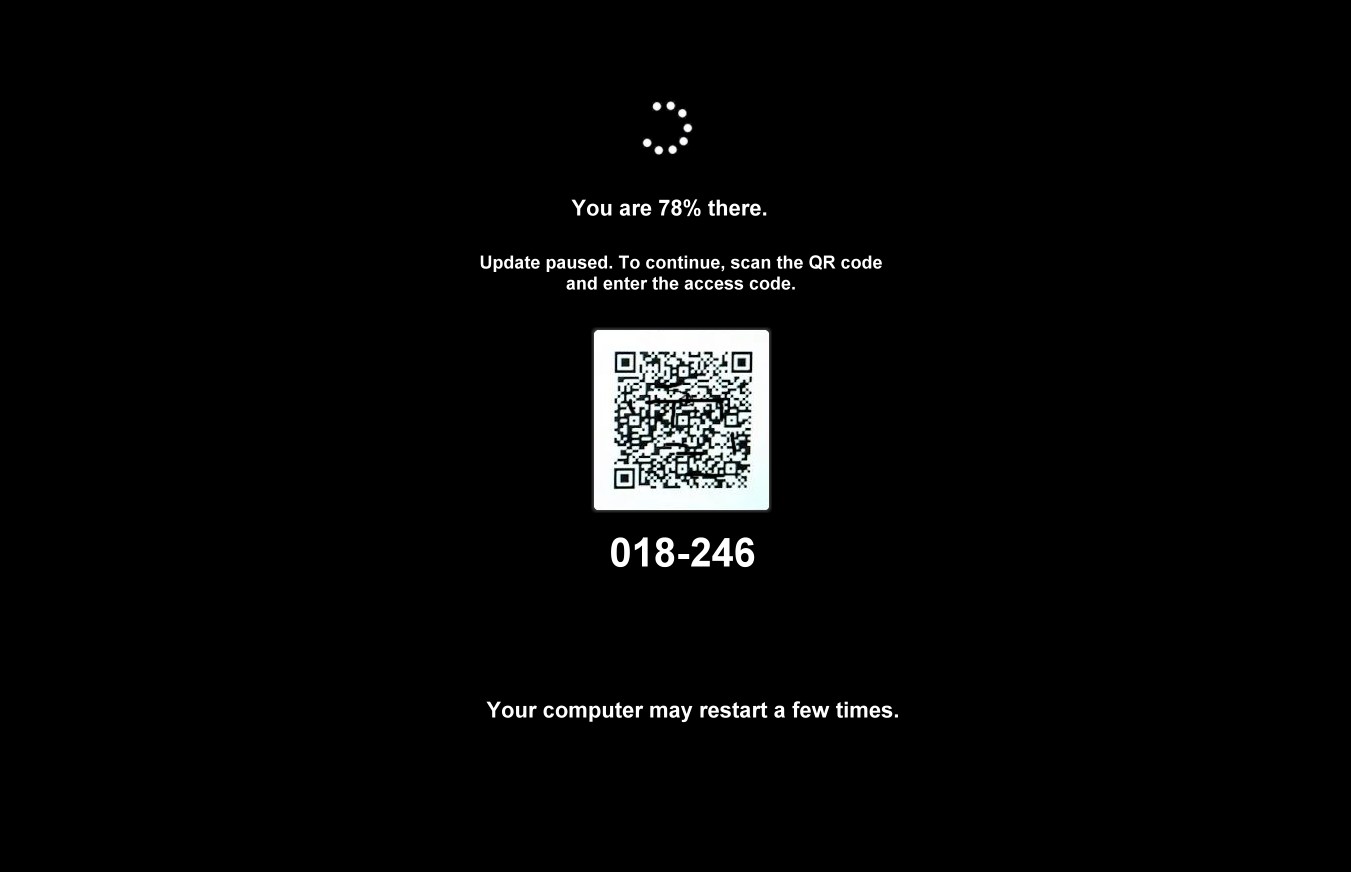
Fake warning: . What if you get an email from Best Buy's Geek Squad that looks like an invoice for services or a plan that you owe money? Are you going to call the phone number or reply so you can get it all straightened out? Better think carefully and act slowly. Sharpen up your BS filter because it's most likely a scam. Here's what can happen with ANY scam where something happens (fake warning, concerning email, bank alert, phone scam). They call you or you are tricked into calling them. You follow instructions and let an "official tech person" help you with whatever issue they are scaring you with. When he gets on your computer, he installs hidden remote desktop software that allows him access at anytime, he then changes or adds a login password and then he wants your credit card for services. By then, you get spooked and realize it's a scam and you hang up. The next time your computer is shut down and restarted, it's locked out wanting a password. You look at your call history, call the number back and this time he wants you to go get money cards from Walgreens. Someone has been in your computer and might have locked you out. Please don't try to solve this on your own because even after you pay potentially hundreds, you will still be locked out. It's a simple trick but if you don't know how it works and how to remove it, it's not so simple. Look out! Here's something new. The two below are not from Windows. The remote "tech" is doing some funny business and the "wait" graphic is hiding his actions. If you see one of these two below, you should power your computer down immediately. They are not real - these screens act as a curtain for the scammer.
Phone Calls From "Microsoft" Another fake. Microsoft doesn't call anyone and they do not have your phone number. Another attempt to trick the user into letting someone into their system who will want to charge money to "fix" it. It's a simple confidence scam where the scammer gains access to the owner's machine with their permission and once connected, they change your password so that once your computer is turned off and restarted, you can't get back in. They do it right in front of your eyes but you won't know what it is until it's too late.
By now, this should be a
no-brainer. Do not ever, ever give anyone your personal
information over the phone or even put it in a web site unless you are
absolutely certain the call is legit (meaning YOU initiated the call to
a number YOU had) or the web site is legit (eg.
www.amazon.com). Not common currently but these get on your system when you interact with an email attachment and attempting to view a zipped PDF. CryptoLocker and other data-encrypting malware are the worst ones I've seen. These actually destroy your personal data like pictures and documents and offer to restore them after you pay a high ransom (hundreds) which may or may not work. The user gets tricked into running the installer by way of an Internet script-based tripwire loaded from an ad or more often from an enticing email attachment pretending to have a report from FedEx, UPS, USPS, PayPal, your ISP, the IRS, etc.. The installer file is activated, the single-file launcher application is placed in a hidden directory and the single-line instruction is added to the registry. Then it runs from inside and begins to encrypt certain file types. Encryption means your files are locked. The files this one goes after are your important personal data like office documents and pictures. Sometimes the files are encrypted and then your antivirus detects and removes the program. If this happens, you won't get an announcement or a way to pay ransom. Protection: What if you already have it? If you get CryptoLocker or CTB-Locker and your files are worth the ransom it is requesting, the malware files(s) and associated registry entries holding part of the encryption key must not be removed until after the ransom has been paid and your files are decrypted. There are people who have reportedly paid the ransom and have had at least some of their data successfully unlocked. Again... once tricked, the only way to regain access to locked data is to pay the ransom as instructed by the malware's splash screen:
Data Protection. An important general safeguard is keeping your data backed up and protecting it with the right method. I have a section about backing up data on my Computer Tips page but unless you know how CryptoLocker works and take extra precautions, your backed up data may not be safe from it. From what I have read from IT professionals and those who have experimented with this rattlesnake, the encryption path follows drive letters and encrypts common personal data files it finds on that path. Meaning if you use an external backup drive and it is connected to your computer using an assigned a drive letter or you have manually created a network share on another computer and mapped it using a drive letter, CryptoLocker can find the drive or shared folder and encrypt the data THERE as well. To check if your external data is vulnerable, go to Computer (My Computer) and if your backup destination sits on the same page as your C: drive and has a drive letter (e.g. E:, F:) or is mapped with a drive letter, your data is not safe. Here's an important thing to remember... if you have an automated backup program and it runs after your local files are encrypted, those backup files can be replaced with encrypted versions. So if you get CryptoLocker, immediately remove the connected destination drive you use for backups or disable your cloud-based backup until your computer is clean. My recommendation is to use more secure data backup and storage options which include using Network Attached Storage (NAS) instead of a USB or firewire-connected external drive. If you have mapped network shares that are on host servers, remove the drive-letter maps and use UNC shortcuts (\\%host computer%\%network share%) instead. Of course burning your data to a recordable CD or DVD is safe, albeit outdated and cumbersome, just be sure to remove the disk from the tray if it is not finalized and closed by your disk-burning software. My personal NAS choice is a Synology DS213j which is a dual-disk unit already configured for RAID 1 (mirrored). The NAS is connected to your router by Ethernet cable and is accessible by approved computers on your network. Note that these units do not normally come with hard drives - you typically add those yourself. The total cost of a NAS storage system is the enclosure plus the drives. If you have a USB drive you
are using for backups and
replacing it is not feasible, physically disconnect it from your computer when it
is not being accessed during backups. |
||
|
|
||
|
|
||